Security Assessment & Validation
Evaluate websites, APIs, networks and infrastructure through vulnerability assessment, penetration testing and security reviews. Receive validated findings, remediation recommendations and agreed retesting.
Understand your risks. Strengthen your defences. K Ocean helps Hong Kong organisations assess systems, monitor threats, govern AI use and protect their digital presence. Start with the security problem you need to solve; we will help define a practical scope and next step.
A Cyberport incubatee with experience across public-sector organisations, enterprises, financial services and insurance.
Security assessment, managed detection and response, AI governance and brand protection, scoped around your systems and business priorities.
Evaluate websites, APIs, networks and infrastructure through vulnerability assessment, penetration testing and security reviews. Receive validated findings, remediation recommendations and agreed retesting.
Strengthen detection and response with 24/7 SOC, managed security and MDR services. Agree monitoring coverage, investigation, escalation and response responsibilities.
Build evidence for security reviews and audit preparation through SRAA, privacy impact assessment, control reviews and ISO 27001 internal-audit preparation.
Assess risks in AI agents, LLM applications and GenAI deployments. Review AI-use policies, sensitive-data handling and control evidence through a scoped assessment or pilot.
Monitor agreed sources for phishing domains, impersonation websites and brand misuse. Human verification, evidence collection and escalation support a documented response.
Test prevention, detection and response through authorised red/blue team exercises, threat-intelligence-based attack simulation and phishing drills. Turn findings into improvement priorities.
Illustrative service imagery.
Explore SolutionsPreparing to launch, reviewing periodically or responding to customer requirements? Start with assets, roles and testing objectives.
Explore serviceEvaluate endpoint, server, mobile, network and application protection against your existing tools, operating needs and deployment requirements.
Endpoint detection and response, antivirus and host-based intrusion detection for user devices and servers.
Firewalls, web application firewalls, intrusion detection and prevention, and network detection and response.
Evaluate selected China-developed security products, with compatibility assessment, deployment planning and staged migration support.
Smart Alternative includes selected China-developed products. Compatibility, data flows, support and migration requirements are assessed for your environment.
Explore ProductsExplore software capabilities for testing, security operations and AI governance. Confirm versions, integrations and deployment requirements through technical scoping.
Review website security assessment capabilities and discuss your assets, testing objectives and reporting requirements with our team.
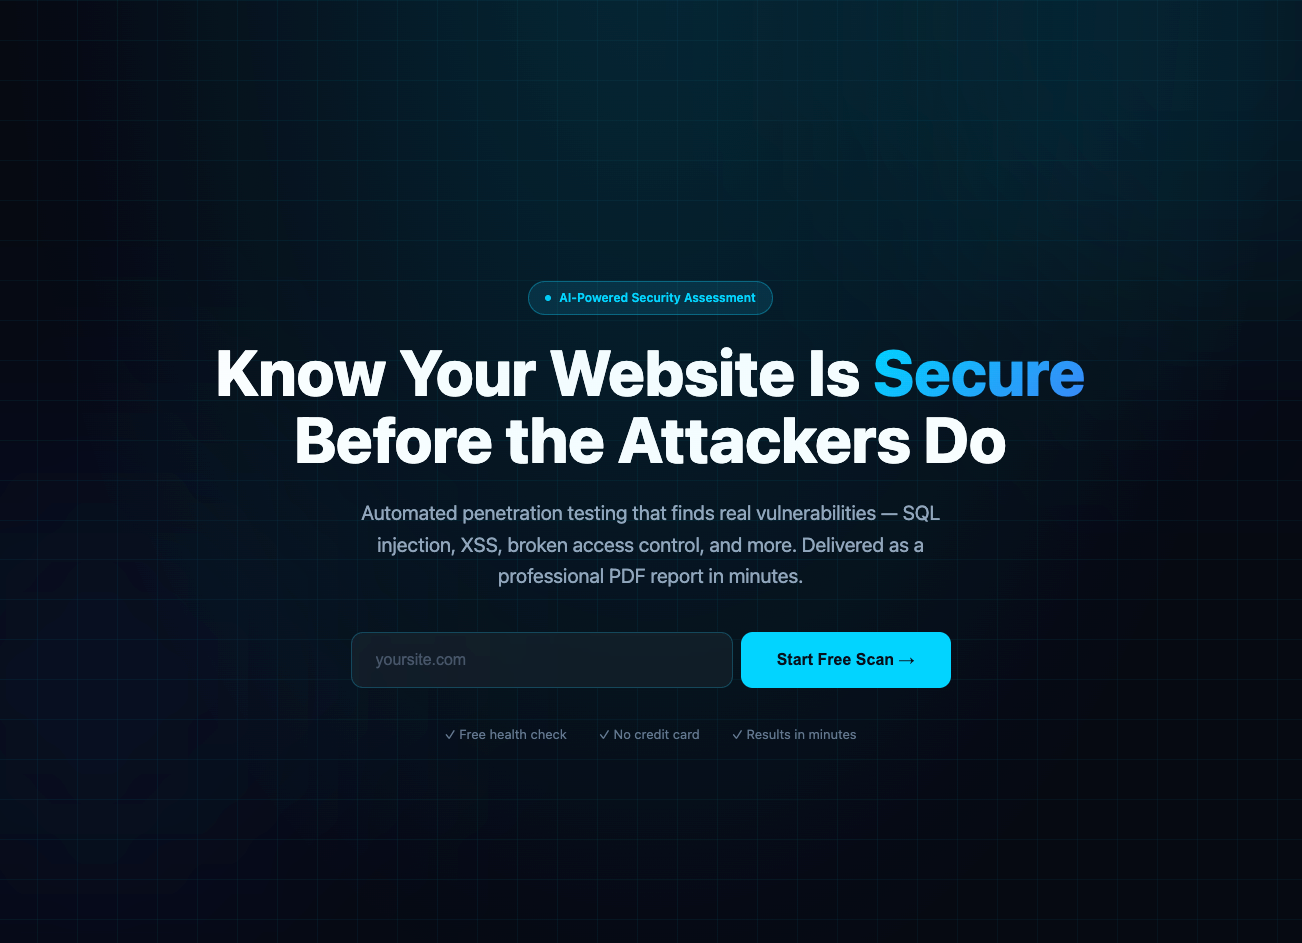
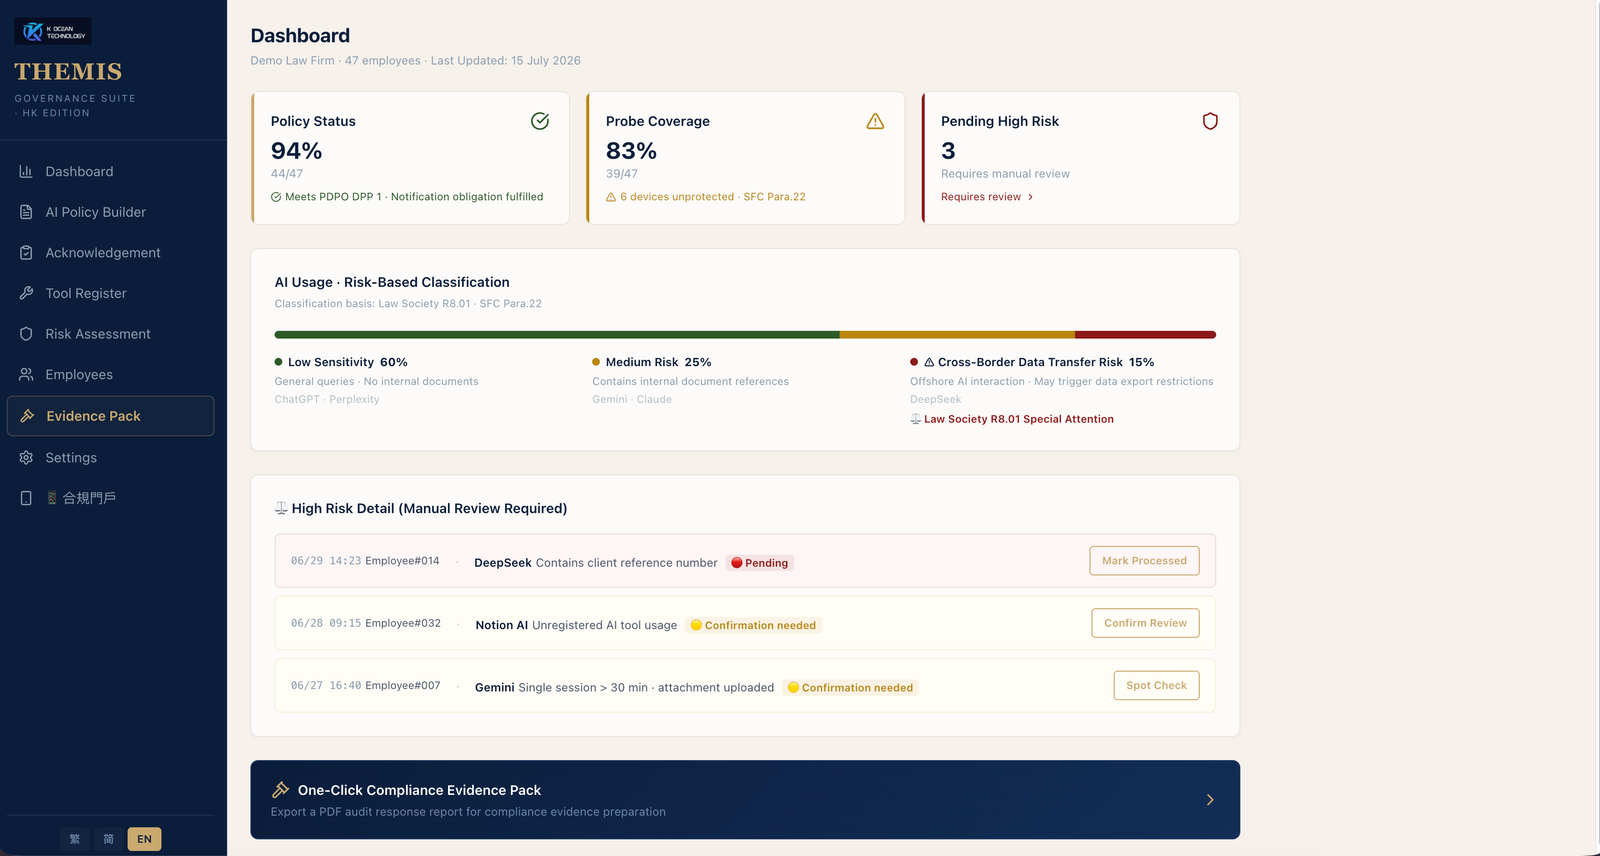
Explore AI-use policy management and reviewable control evidence. Assess browser, endpoint and gateway controls through a defined pilot.
Combine AI-assisted discovery and testing with senior red-team judgement. Agree authorisation and scope, validate findings and review the evidence before remediation and retesting.
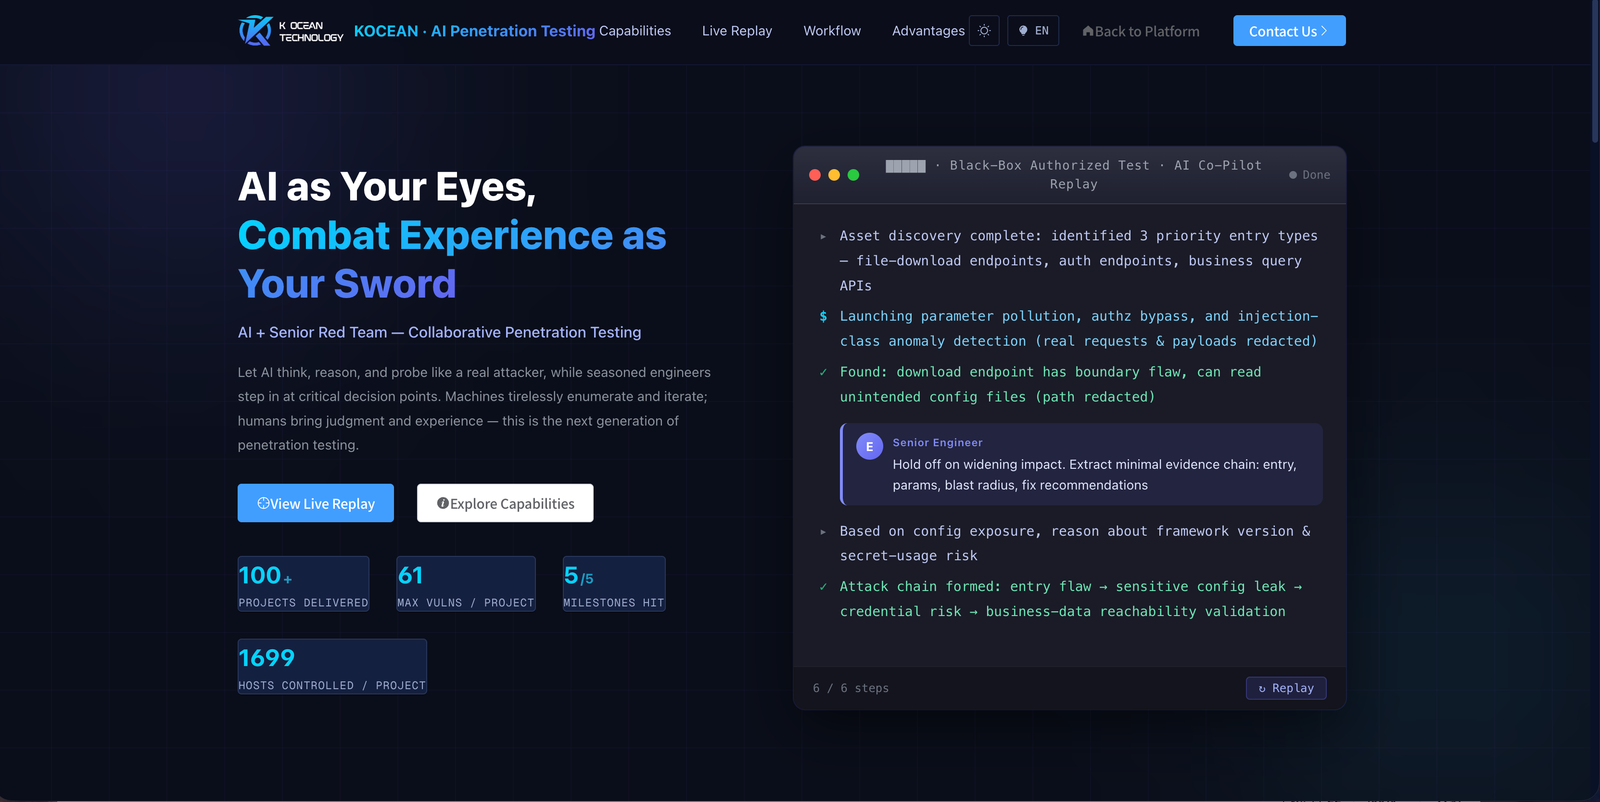
Product screens supplied by K Ocean. THEMIS dashboard figures are demonstration data.
Capabilities and availability depend on the selected version and agreed deployment. Evaluation and pilot scope are agreed before deployment.
Explore PlatformsSupporting organisations with complex systems, sensitive information and demanding assurance requirements.
Offensive and defensive cybersecurity exercises, security assessment and technical advisory support.
Application and infrastructure testing, remediation verification, security technology and operational support.
Security assessment, risk reviews and evidence to support audit preparation.
Independent cybersecurity validation and threat-intelligence-based attack simulation.
Know what will be assessed, delivered and verified before an engagement begins.
Agree assets, objectives, authorisation, data boundaries and acceptance criteria.
Combine appropriate tools with manual investigation and technical judgement.
Explain the evidence, business impact and recommended actions.
Retest agreed findings and record what is fixed, unresolved or not yet verified.
Practical cybersecurity guides, company news and conversations from our community.
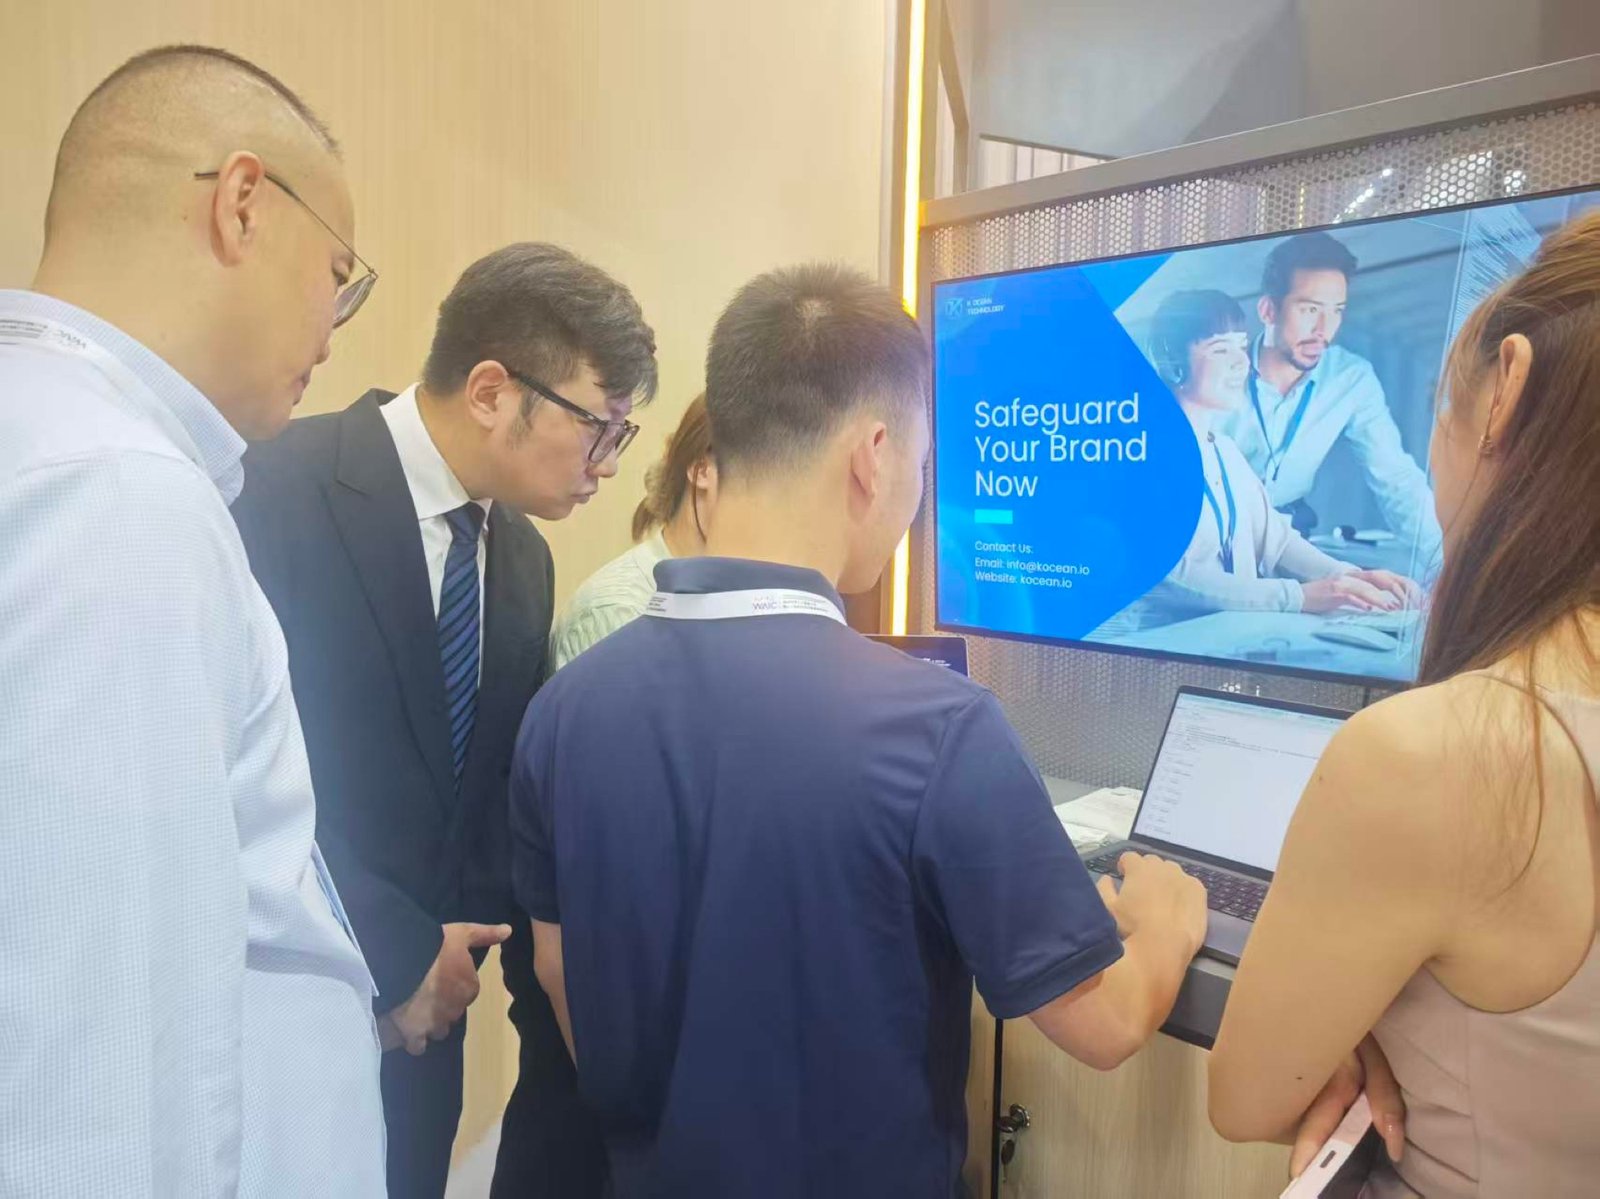
In Shanghai, K Ocean joined the Hong Kong Tech Pavilion to discuss AI security, assessment, monitoring and digital risk.
Read article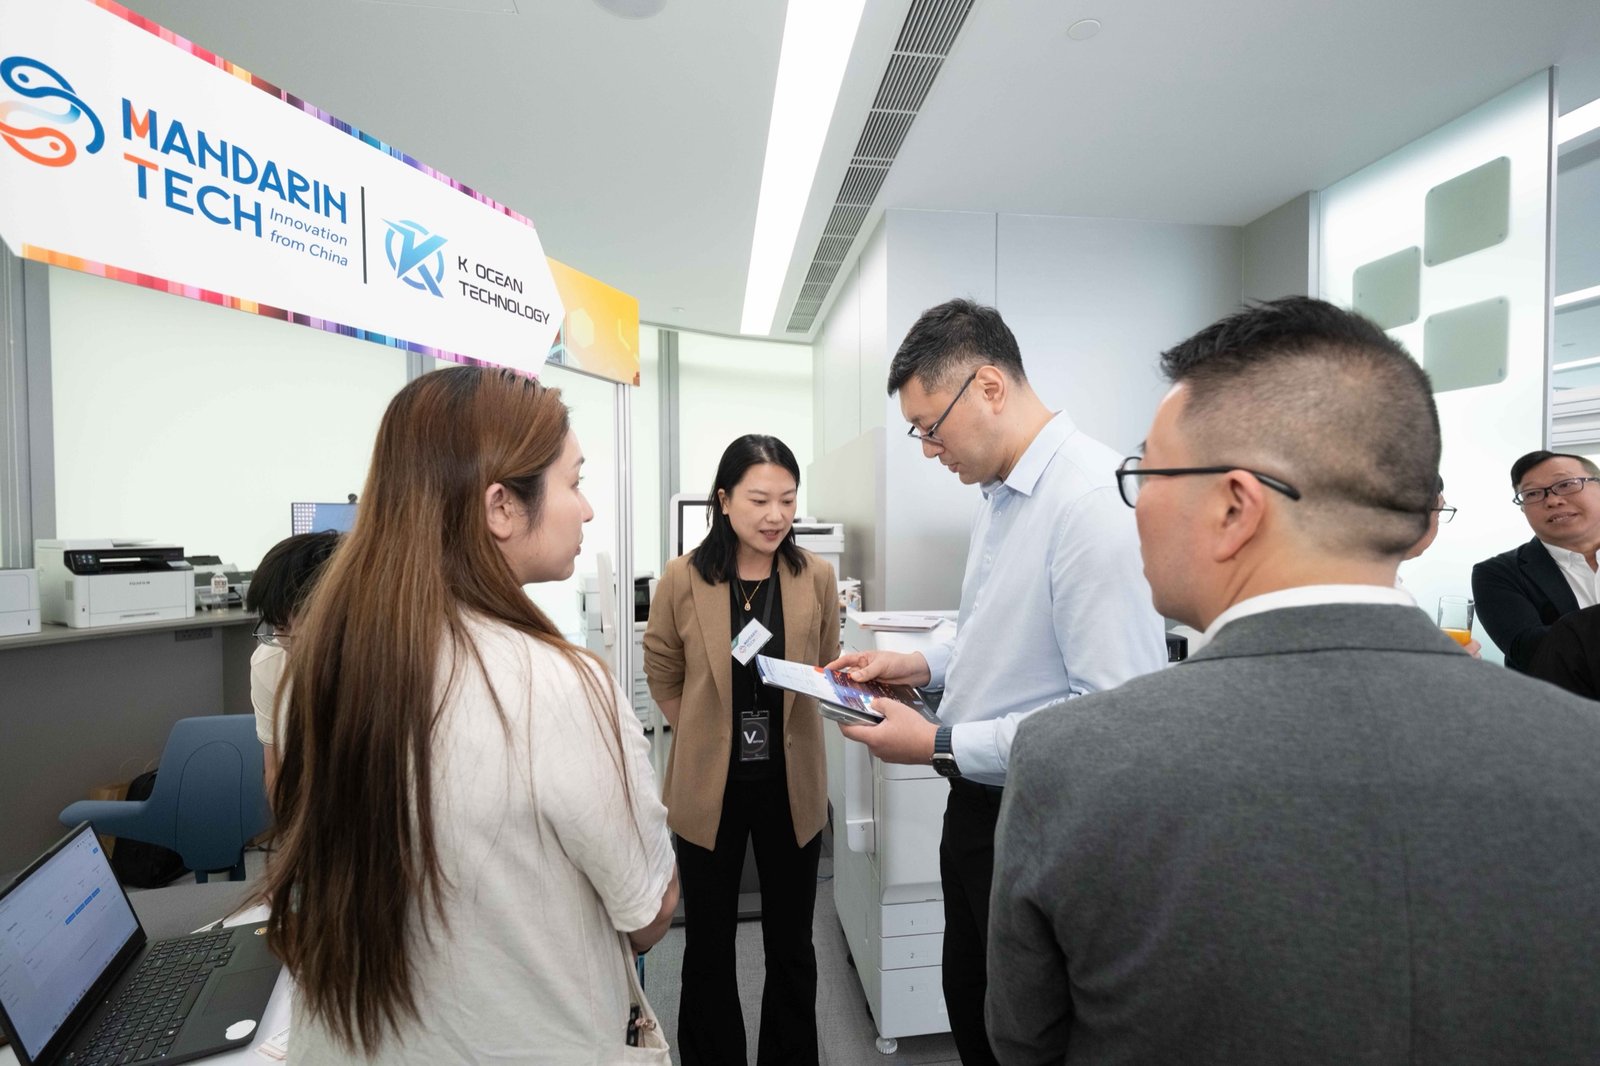
K Ocean joined the Hong Kong seminar for conversations on resilience, hidden attack surfaces and the integration of technology solutions.
Read articleA practical guide to monitoring, human verification and a coordinated response to fake websites, phishing domains and social impersonation.
Read articleClear answers to common questions about assessment, monitoring, AI governance, brand protection and endpoint security.
View all questionsStart with the business concern, affected systems and existing controls. An initial discussion helps identify whether you need a focused test, a wider risk review, monitoring support or a product evaluation. You do not need to choose a platform first.
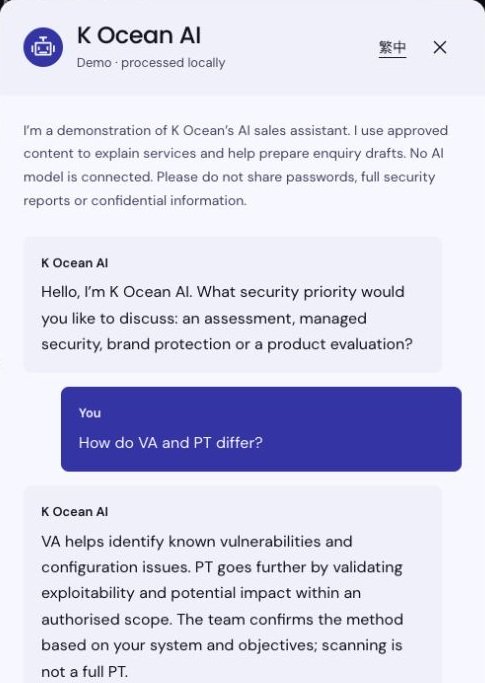
Vulnerability assessment identifies and assesses potential weaknesses. Penetration testing examines agreed attack paths and validates relevant findings through authorised testing. The appropriate combination depends on the assets, objectives and access available.
No. Monitoring coverage is part of the agreed service. Discuss the systems, telemetry, staffing window, escalation and response requirements. Any 24/7 coverage or response commitment must be stated in the engagement terms.
Yes. We can discuss approved-tool policies, sensitive-data handling, access controls and reviewable governance evidence. The appropriate controls depend on your workflows, chosen tools and deployment. A governance product alone does not establish compliance.
No. Verification and evidence support reporting and authorised coordination, but removal decisions depend on external providers and applicable processes. We agree monitoring coverage and response responsibilities before starting.
Support depends on the selected product edition and configuration. Confirm device types, operating-system versions and management requirements before purchase or deployment. Mobile protection and desktop/server EDR should not be treated as identical products.
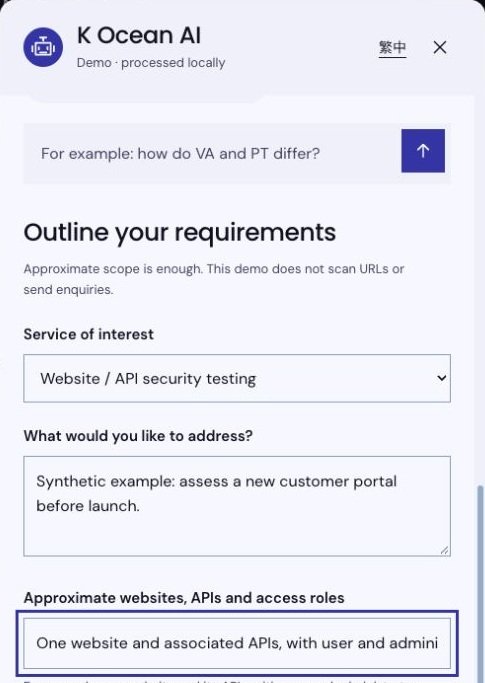
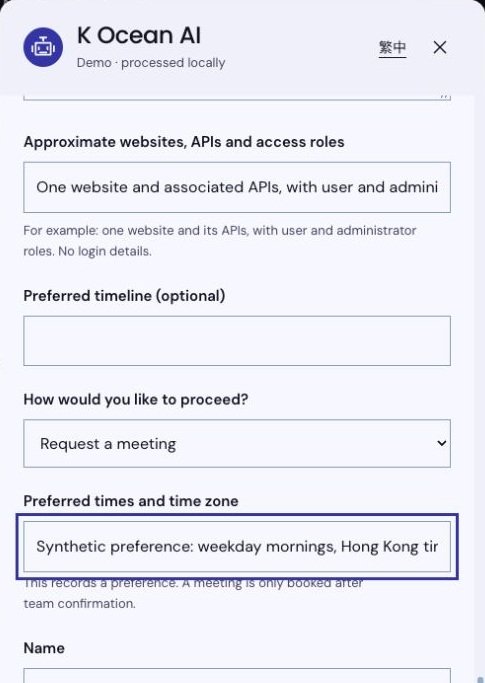
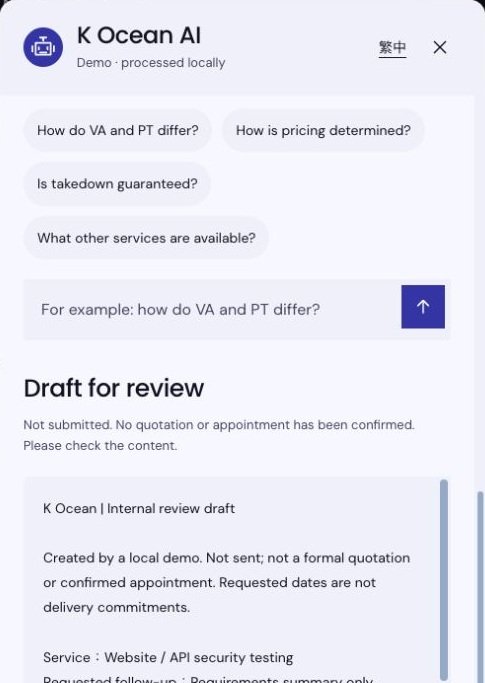
K Ocean AI helps explain services and organise your requirements into an enquiry, meeting request or quotation draft for team review.
Local prototype screens · synthetic examples · no enquiries sent
Start with an assessment, stronger detection and response, or a product evaluation. Our team confirms scope, pricing and appointments.
System integration partners: FUJIFILM Business Innovation Hong Kong · NEXIFY · Konica Minolta · Kyocera
View clients & partnersLocal demo · no messages sent