Cybersecurity health check
Changing IT providers, moving a system to the cloud or answering a customer security review? Start by identifying the risks to the systems your business depends on.
Start with a cybersecurity health check or scope a formal SRAA. We also assess privacy risks and help teams monitor external threats.
Security Risk Assessment and Audit (SRAA)Changing IT providers, moving a system to the cloud or answering a customer security review? Start by identifying the risks to the systems your business depends on.
Start with a health check when you need to identify which risks to address first. If a tender or customer specifies audit criteria or a report format, share those requirements so we can scope an SRAA.
Review security risks and control evidence for an agreed system. Get a prioritised action list for management, a tender response or a system launch.
Contact K OceanReview how your project collects, uses, shares and retains personal data. Identify privacy risks and safeguards before launch or a major change.
Contact K Ocean
Review security risks and control evidence for an agreed system. Get a prioritised action list for management, a tender response or a system launch.
Evaluate websites, APIs, networks and infrastructure through vulnerability assessment, penetration testing and security reviews. Receive validated findings, remediation recommendations and agreed retesting.
Explore service
Strengthen detection and response with 24/7 SOC, managed security and MDR services. Agree monitoring coverage, investigation, escalation and response responsibilities.
Explore service
Assess risks in AI agents, LLM applications and GenAI deployments. Review AI-use policies, sensitive-data handling and control evidence through a scoped assessment or pilot.
Explore service
Monitor agreed sources for phishing domains, impersonation websites and brand misuse. Human verification, evidence collection and escalation support a documented response.
Explore serviceExplore K Ocean Pro
Test prevention, detection and response through authorised red/blue team exercises, threat-intelligence-based attack simulation and phishing drills. Turn findings into improvement priorities.
Illustrative service imagery.
Assess your own systems or investigate risks outside your network.
Website and API VA / PT to identify weaknesses, understand impact and plan remediation with agreed retesting.
Explore serviceIllustrative footage · 10 seconds
Monitoring for fake websites and phishing domains, with human verification and evidence to support your response.
Explore serviceIllustrative footage · 10 seconds
Know what will be assessed, delivered and verified before an engagement begins.
Agree assets, objectives, authorisation, data boundaries and acceptance criteria.
Combine appropriate tools with manual investigation and technical judgement.
Explain the evidence, business impact and recommended actions.
Retest agreed findings and record what is fixed, unresolved or not yet verified.
Clear answers to common questions about assessment, monitoring, AI governance, brand protection and endpoint security.
We provide assessment and testing, managed security, AI governance, brand protection and endpoint-security support. Risk assessments, privacy reviews, exercises and training are scoped to the engagement.
Start with the business concern, affected systems and existing controls. An initial discussion helps identify whether you need a focused test, a wider risk review, monitoring support or a product evaluation. You do not need to choose a platform first.
Vulnerability assessment identifies and assesses potential weaknesses. Penetration testing examines agreed attack paths and validates relevant findings through authorised testing. The appropriate combination depends on the assets, objectives and access available.
Agreed deliverables can include reviewed findings, evidence, risk priorities and remediation recommendations. Retesting records what was checked, its result and limitations within the assignment.
Yes. We can define responsibilities alongside your internal team, outsourced provider or both. Agree access, coordination, remediation ownership and escalation routes before work begins so that findings can lead to action.
No. Monitoring coverage is part of the agreed service. Discuss the systems, telemetry, staffing window, escalation and response requirements. Any 24/7 coverage or response commitment must be stated in the engagement terms.
No. AI-assisted testing uses AI to support assessment work. AI-application security assessment examines risks in an AI-enabled system, such as its permissions, data access and integrations. The test plan must identify which service you need.
Yes. We can discuss approved-tool policies, sensitive-data handling, access controls and reviewable governance evidence. The appropriate controls depend on your workflows, chosen tools and deployment. A governance product alone does not establish compliance.
No. Verification and evidence support reporting and authorised coordination, but removal decisions depend on external providers and applicable processes. We agree monitoring coverage and response responsibilities before starting.
Support depends on the selected product edition and configuration. Confirm device types, operating-system versions and management requirements before purchase or deployment. Mobile protection and desktop/server EDR should not be treated as identical products.
Yes. We can describe sector, challenge, work and deliverables anonymously. Named references and logos require publication approval. Individual results are not universal promises.
Share an approximate number of websites, APIs or network assets, user roles, the test environment and your target date. K Ocean confirms authorisation, access, reporting and retesting scope before quoting. Do not send passwords, production credentials or confidential reports in an initial enquiry.
The schedule depends on the number of assets and roles, application complexity, available access, testing windows and reporting requirements. K Ocean agrees the test period, report delivery and any retesting after scoping; there is no single duration that fits every assessment.
Coverage can include agreed brand names, fake websites, phishing domains, social profiles and false partnership claims. K Ocean agrees markets and sources, verifies relevant findings and records evidence. Brand monitoring examines external impersonation; penetration testing assesses systems you are authorised to test.
Provide the suspicious URL or profile, the official brand or domain it appears to imitate, and a screenshot or time observed if available. Avoid logging in, paying or downloading files from the suspicious source. K Ocean first reviews the evidence and agrees any further investigation or authorised response.
Yes. Email info@kocean.io or contact K Ocean on WhatsApp at +852 6799 2014 to request a 20–30 minute discussion. Briefly describe your organisation, security concern and preferred times. A colleague confirms the appointment; sending a request does not automatically book a meeting.
Email info@kocean.io or use the website enquiry form to prepare an email draft. Describe your organisation, the service of interest and a brief outline of your needs. The team confirms scope, pricing and demonstration arrangements; an enquiry is not a confirmed booking.
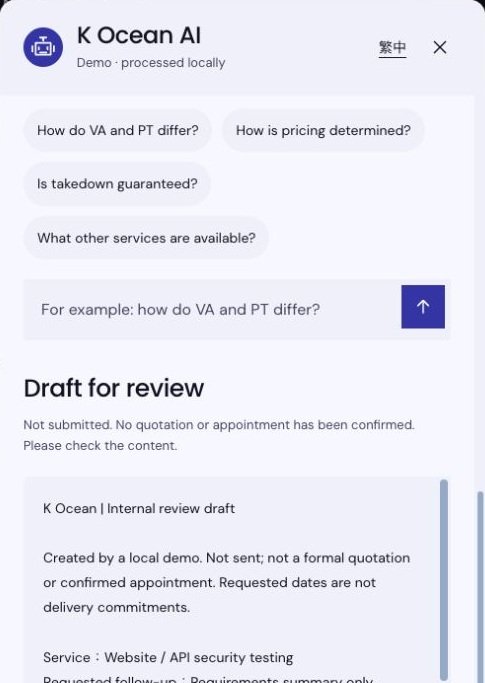
K Ocean AI helps explain services and organise your requirements into an enquiry, meeting request or quotation draft for team review.
Local prototype screens · synthetic examples · no enquiries sent
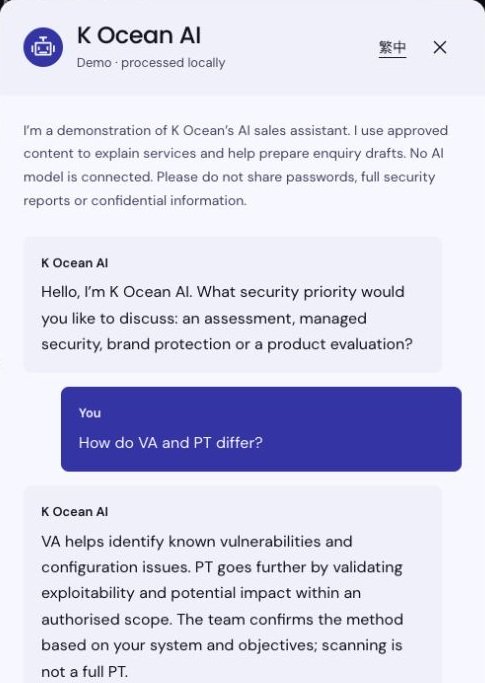
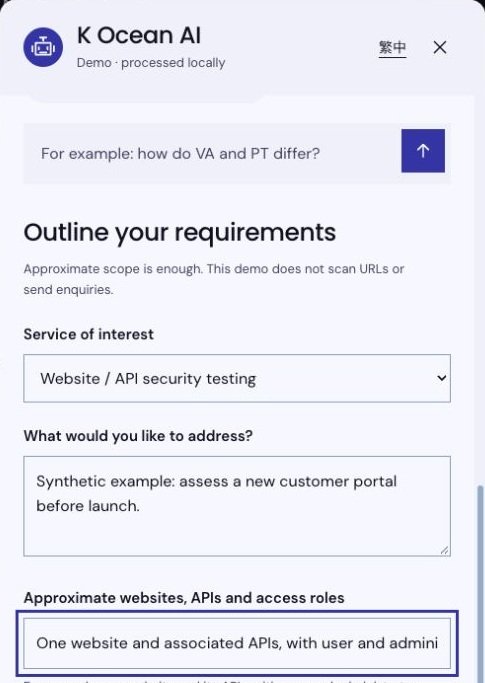
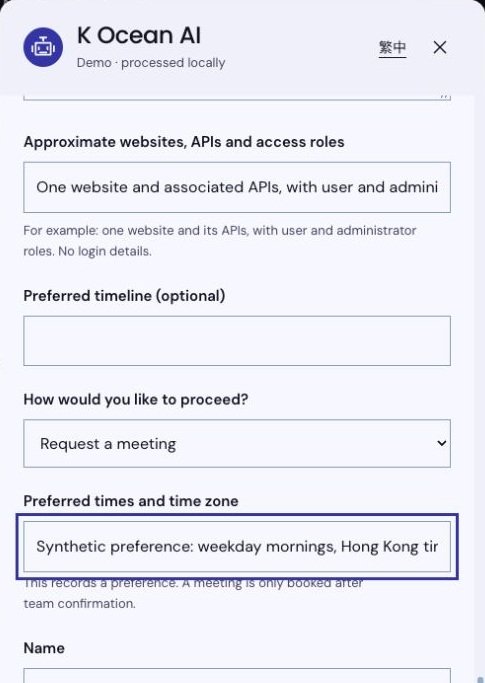
Start with an assessment, stronger detection and response, or a product evaluation. Our team confirms scope, pricing and appointments.
Local demo · no messages sent